02.11.2026 21:50


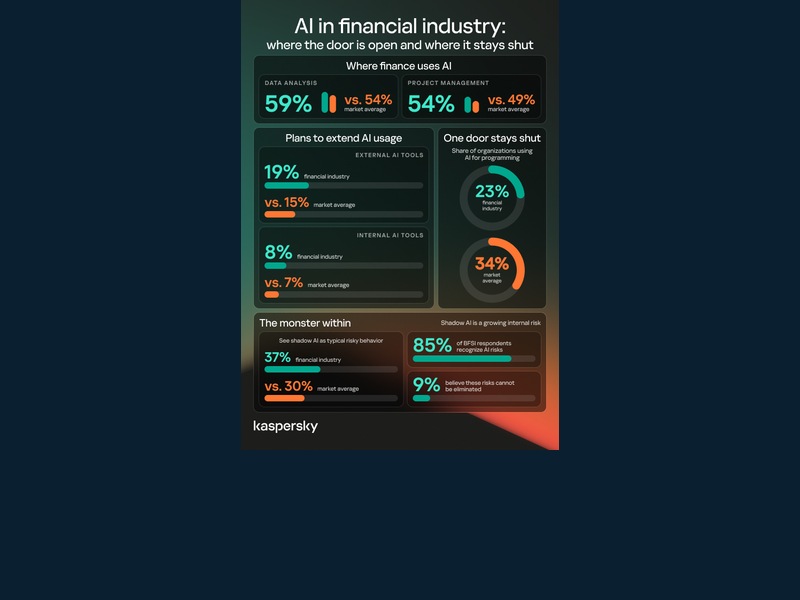
Kaspersky’s financial-sector research reports increasing use of AI in data analysis and project management. The company highlights unapproved tools as a separate issue for data security and access management.
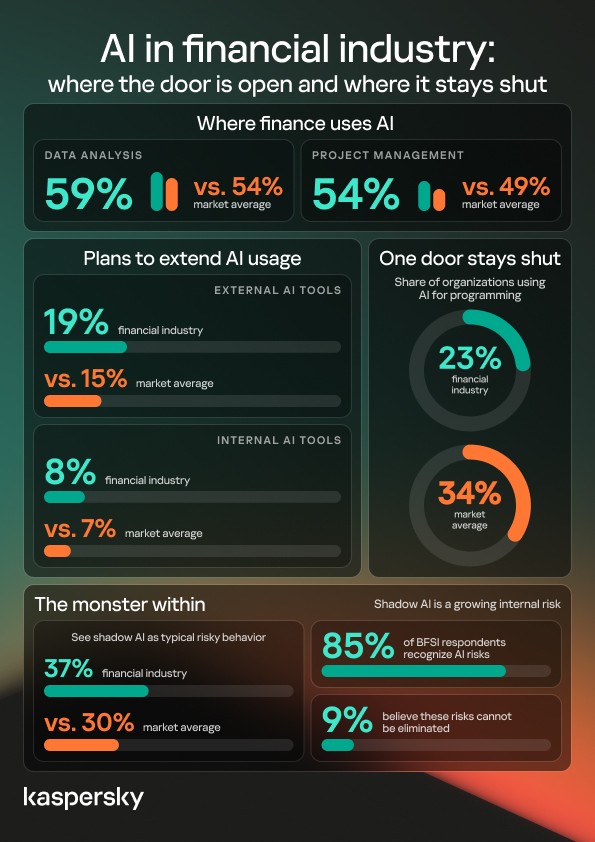
Kaspersky’s research covering banking, financial services and insurance reports AI use for data analysis at 59%, compared with 54% in other sectors. For project management, the financial-sector figure is 54%, against 49% in the comparison group.
These percentages concern the study’s own participants. The release does not provide a detailed sampling and methodology table supporting generalisation to every worker in the sector, so they should be read as the company’s research findings. Widespread use does not establish equal security or business outcomes across applications.
Employees using tools that have not been approved by their organisation is described as shadow AI. The research puts this at 37% in finance and 30% elsewhere. The issue is broader than installing an application: it also concerns which service receives corporate data and under what conditions.
The release says 85% of respondents are aware of this use and 9% regard it as unavoidable. For coding-related AI use, it reports 23% in finance against 34% in other sectors. The range of tasks illustrates why a security policy cannot be reduced to one scenario.
Plans to increase external AI-tool use are reported at 19% in finance and 15% in the comparison group. For internal tools, the figures are 8% and 7%. Intentions need to be distinguished from completed deployments.
Kaspersky recommends clear corporate rules addressing uncontrolled sharing of sensitive data, phishing and fabricated audio or video. Approved-tool lists, minimum necessary access and human review form parts of that approach. A fluent answer is not necessarily financially or operationally correct, so turning an automated output into a business decision requires separate assessment.